MCP Inspector: the Session Token, DANGEROUSLY_OMIT_AUTH and a Local Server
MCP Inspector is the quickest way to poke at an MCP server: list its tools, call one, see the raw result. It speaks stdio, SSE and streamable HTTP. This post builds a small FastMCP server, points the Inspector at it, and explains the session token the Inspector prints when it starts, along with the DANGEROUSLY_OMIT_AUTH switch that turns it off.
Updated October 2026. Inspector 2 (July 2026) changed the ports and renamed the token. Both versions are covered below; the screenshots are from version 1.
A server to inspect
I use FastMCP 2.0. Create a project:
uv init greeting
cd greeting
uv add fastmcp
Put this in main.py:
from fastmcp import FastMCP

mcp = FastMCP("My MCP Server")

@mcp.tool
def greet(name: str) -> str:
    return f"Hello, {name}!"
Run it over streamable HTTP:
uv run fastmcp run main.py --transport httpThe server listens at http://localhost:8000/mcp.
Running the Inspector
You need Node.js (Inspector 2 wants Node 22.19 or newer). Give the Inspector the server’s URL:
npx @modelcontextprotocol/inspector http://localhost:8000/mcpInspector 2 works out the transport from the path: a URL ending in /mcp means streamable HTTP. Anything else, including /mcp/ with a trailing slash, needs --transport http (or sse). You can also start it with no arguments and type the URL into the web page.
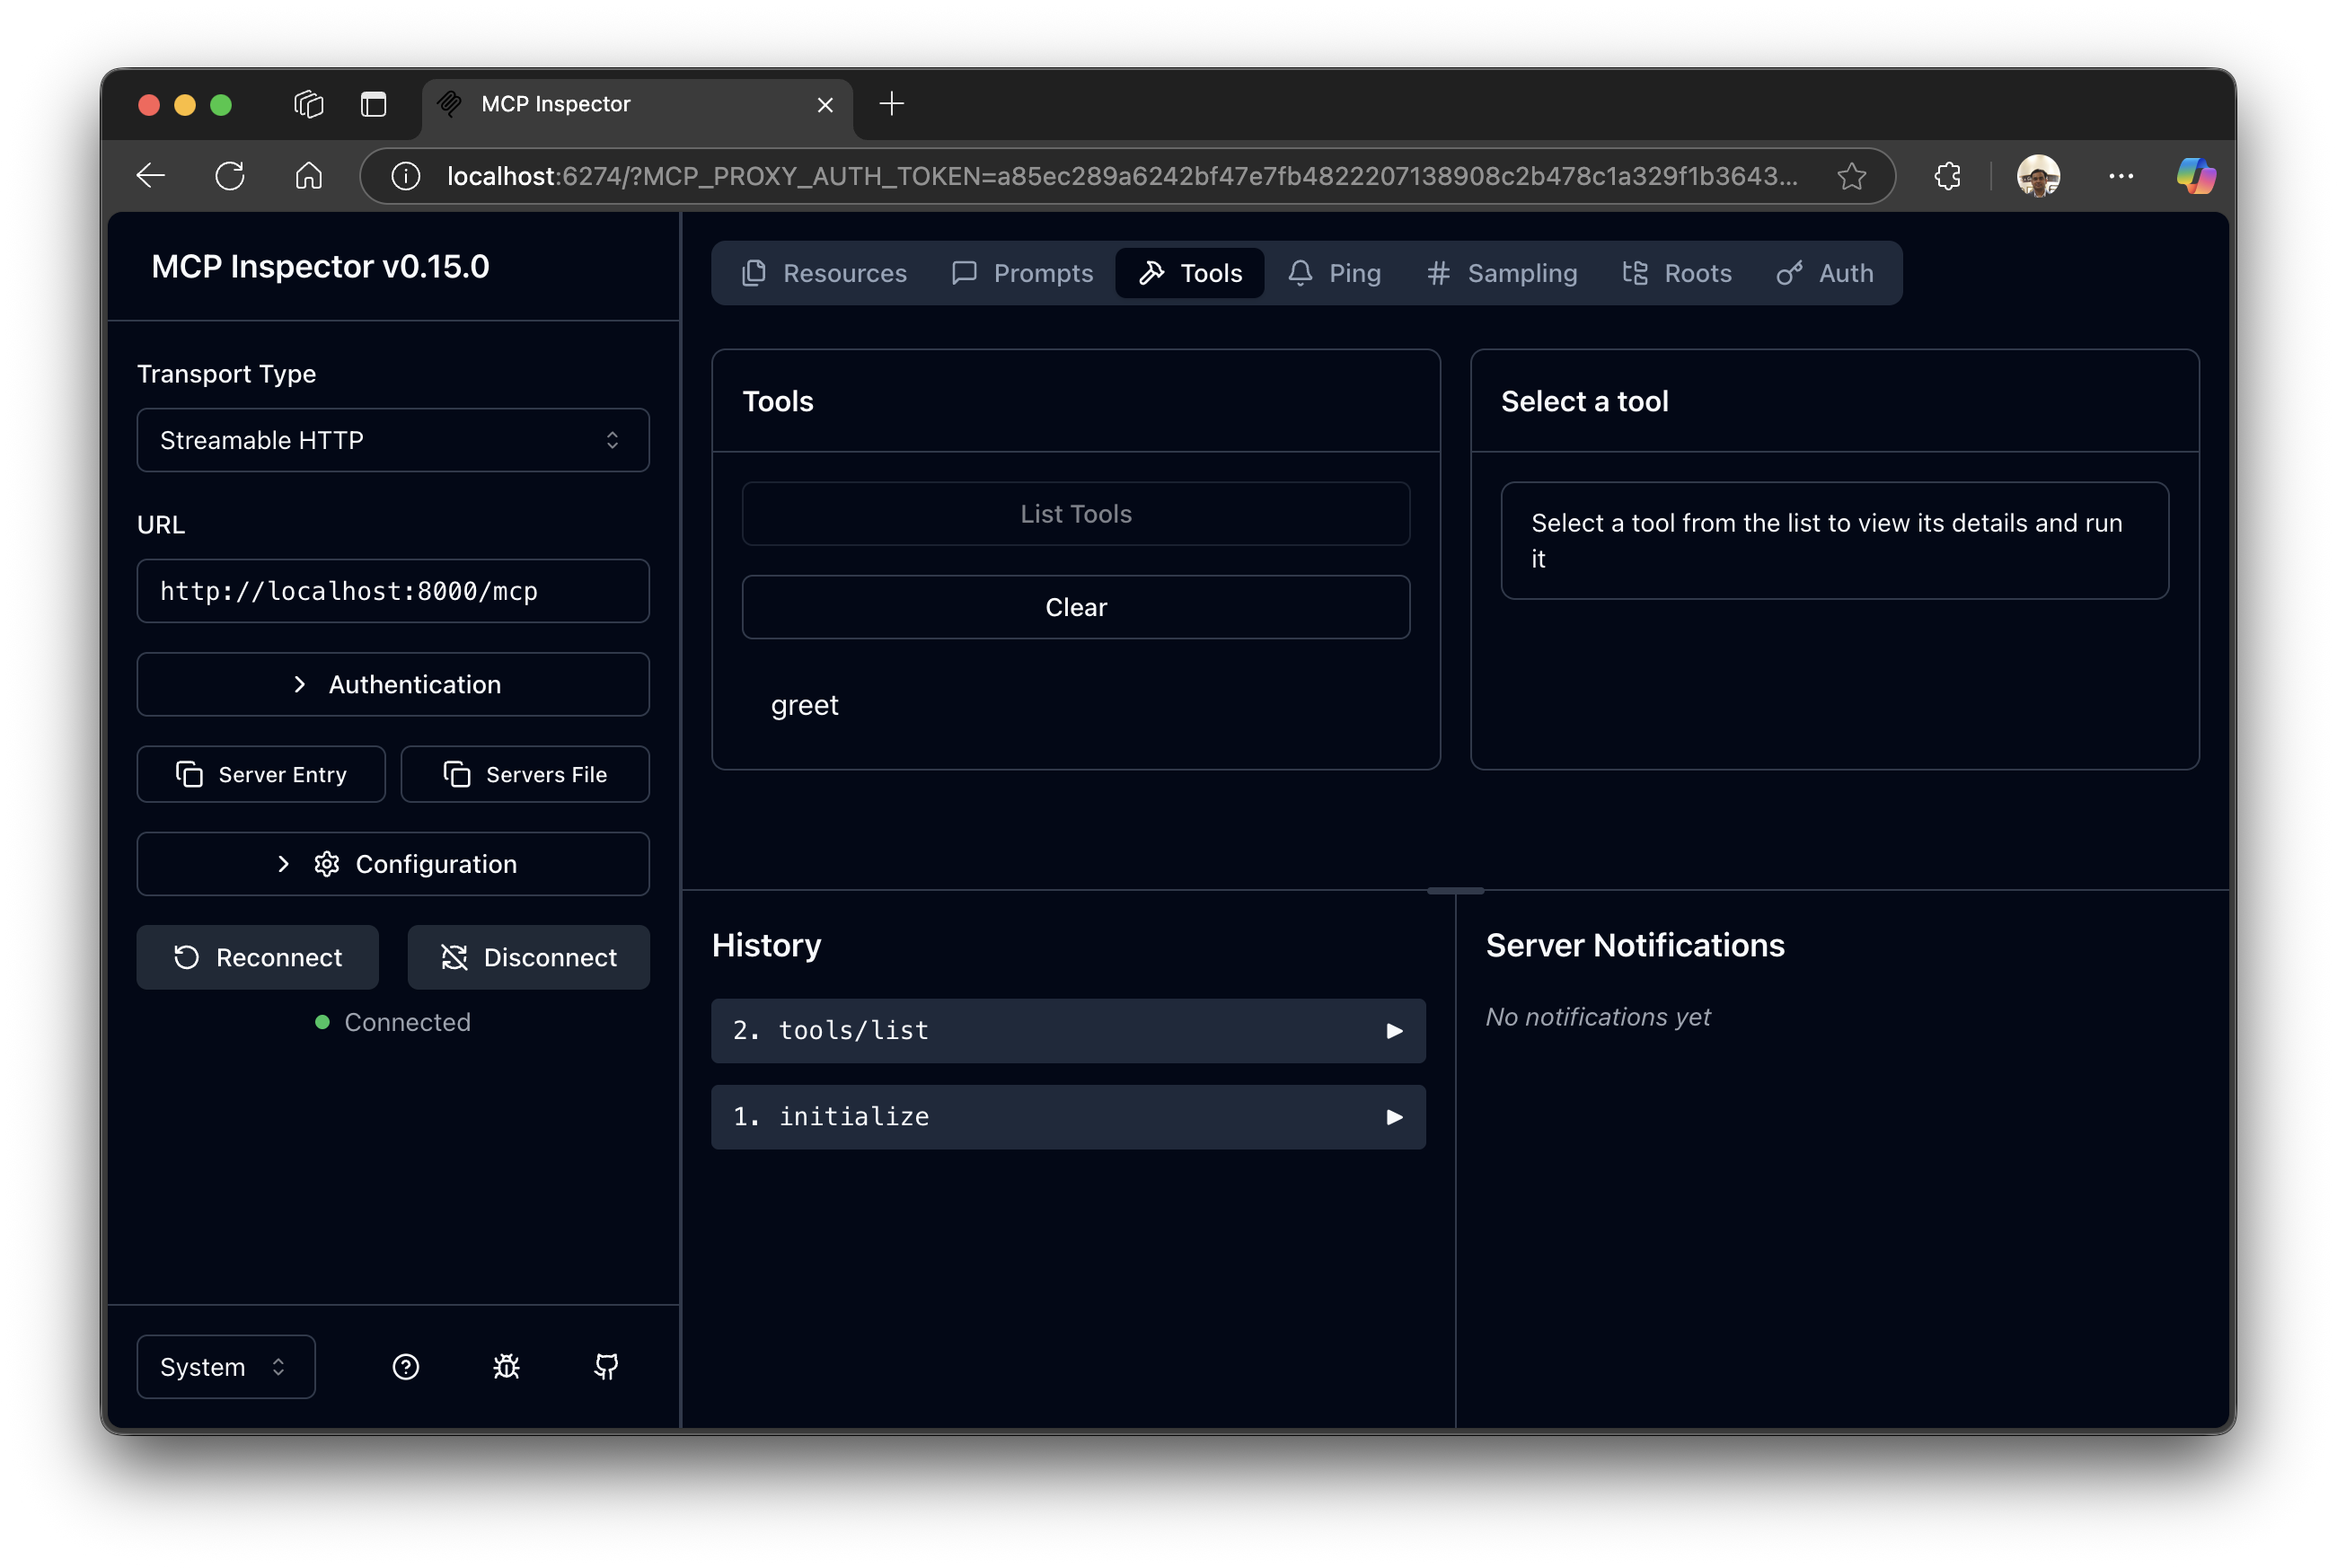
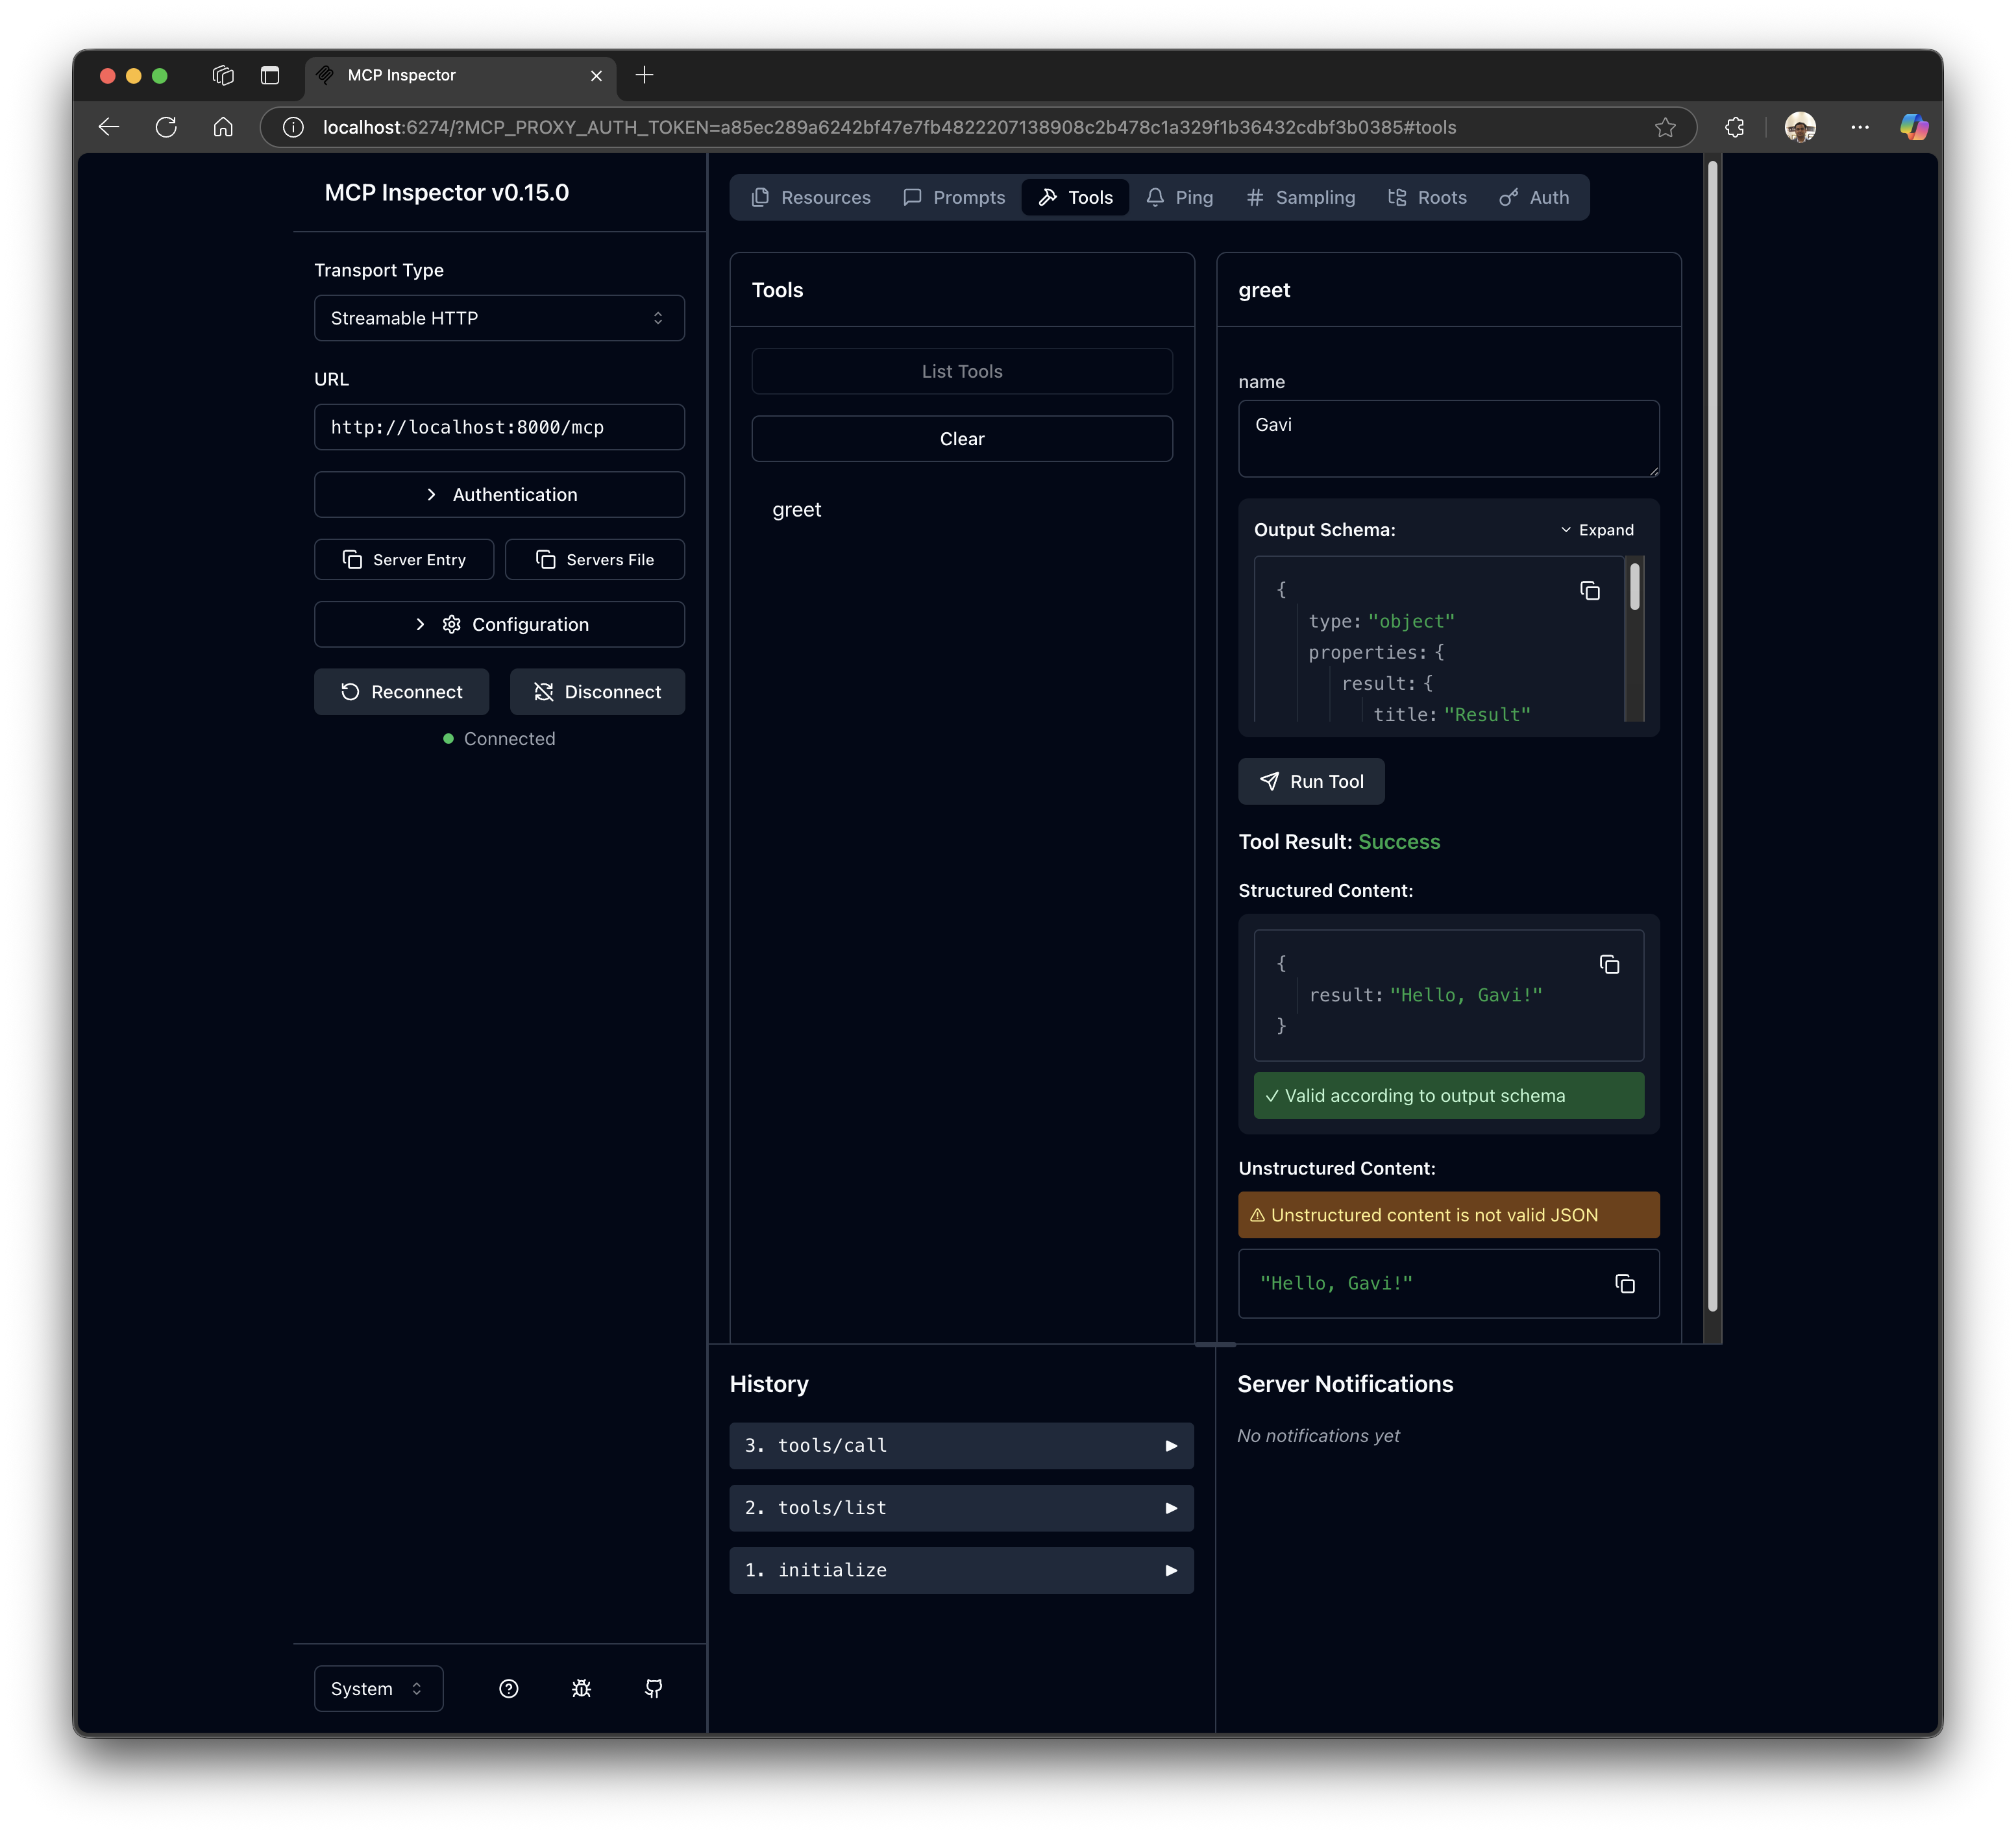
Connect, list the tools, and greet shows up. Pick it, fill in a name, and run it.
The session token
When the Inspector starts, it prints a token and a link with the token already filled in. Inspector 1 printed this:
Starting MCP inspector...
⚙️ Proxy server listening on 127.0.0.1:6277
🔑 Session token: a85ec289a6242bf47e7fb4822207138908c2b478c1a329f1b36432cdbf3b0385
Use this token to authenticate requests or set DANGEROUSLY_OMIT_AUTH=true to disable auth

🔗 Open inspector with token pre-filled:
   http://localhost:6274/?MCP_PROXY_AUTH_TOKEN=a85ec289a6242bf47e7fb4822207138908c2b478c1a329f1b36432cdbf3b0385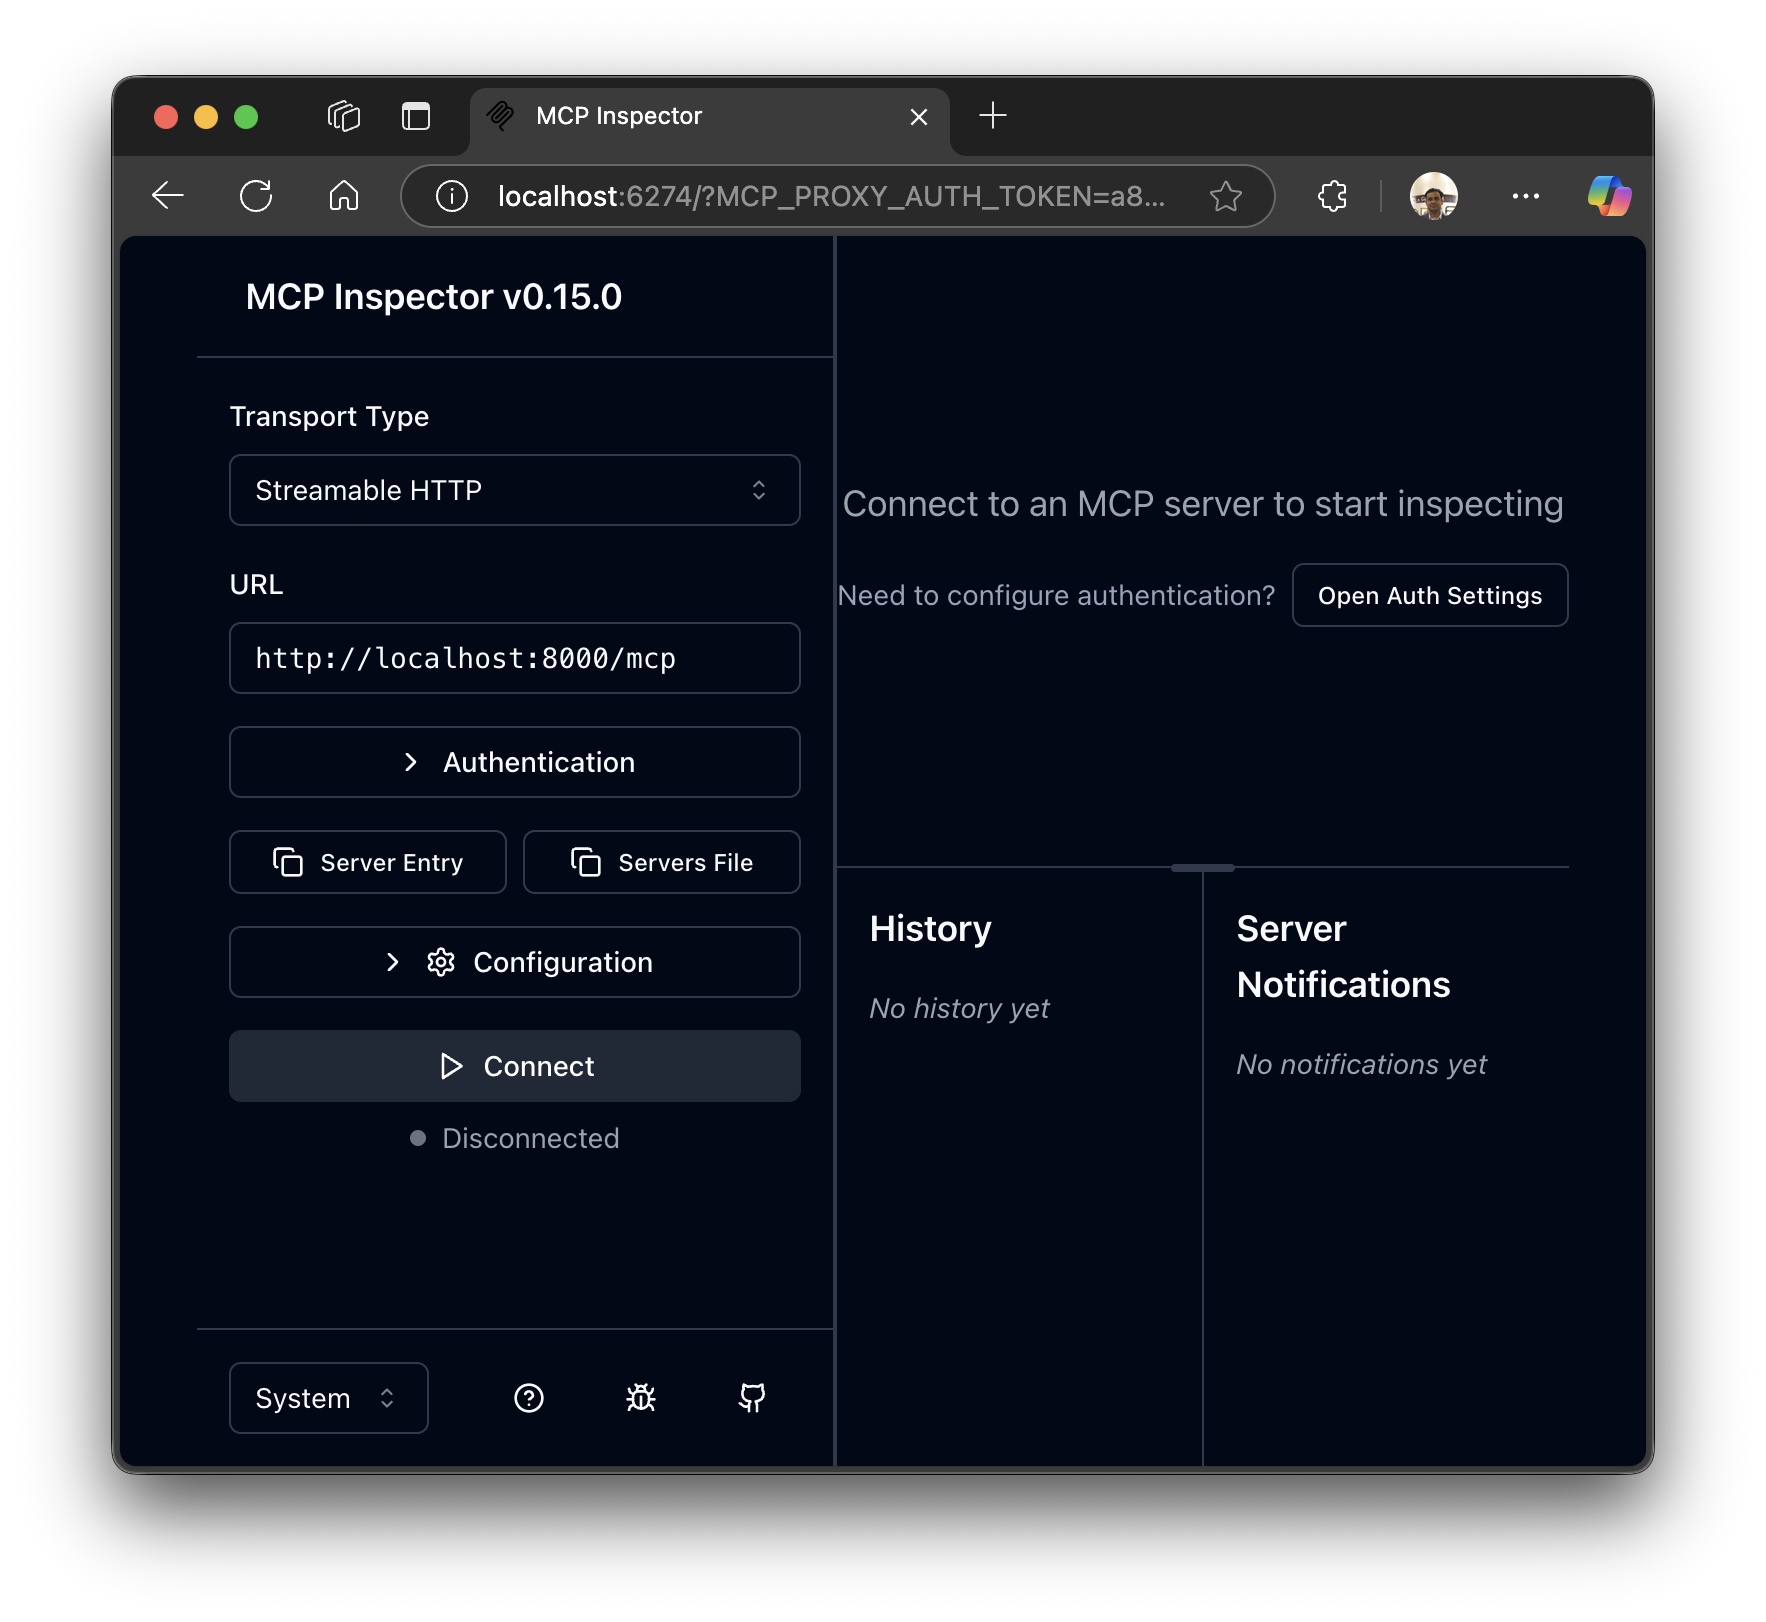
Open that link rather than the bare localhost:6274. If the page complains about a missing or wrong token, that is why.
The token exists because the Inspector can start programs on your machine: a stdio server is a command it runs. Before version 0.14.1 there was no authentication between the Inspector’s page and its proxy, so any website you visited could ask it to launch a command (CVE-2025-49596, June 2025). The token closed that hole.
What changed in Inspector 2:
| Inspector 1 | Inspector 2 | |
|---|---|---|
| Processes and ports | web UI on 6274, MCP proxy on 6277 | one web server on 6274 (plus a sandbox port, 6275, for the MCP Apps tab) |
| Token variable | MCP_PROXY_AUTH_TOKEN |
MCP_INSPECTOR_API_TOKEN (the old name still works as a fallback) |
| Token in the link | ?MCP_PROXY_AUTH_TOKEN=… |
?MCP_INSPECTOR_API_TOKEN=… (the old query parameter does not work) |
DANGEROUSLY_OMIT_AUTH |
any non-empty value turned auth off, even false |
only true or 1 |
DANGEROUSLY_OMIT_AUTH
DANGEROUSLY_OMIT_AUTH=true npx @modelcontextprotocol/inspectorThis turns the token check off. The name is honest: it removes the one check that stops something other than you from driving the Inspector, and through it every server you have configured. I only use it inside a throwaway container whose port is bound to 127.0.0.1, never on a laptop on a shared network. For everything else, the link the Inspector prints does the same job safely.
If you are on Inspector 1 and set DANGEROUSLY_OMIT_AUTH=false thinking it turns auth on, it does the opposite. Unset the variable instead.
OAuth
To try a server that wants OAuth, give the Inspector its URL. Mine is a test identity server at https://idp.objectgraph.com/mcp; how I built a server like it is in Building MCP PyExec. Inspector 2 has OAuth settings per server, saved with the server in its catalog, in place of version 1’s bearer-token field.
What a client has to do when a remote server answers 401 is in MCP server returns 401: implementing OAuth in an MCP client.
